 SOC Project
Wireshark Project

You are a SOC analyst. In this project you will investigate through different lab scenarios. Use Wireshark skills to find the answers about attackers, hidden data, passwords and scam calls. Here, each module/lab has a task box, hints and a step by step solution. Labs 1 to 3 run in your browser with no install and no setup. Labs 4 and 5 run on your own laptop with Wireshark installed.
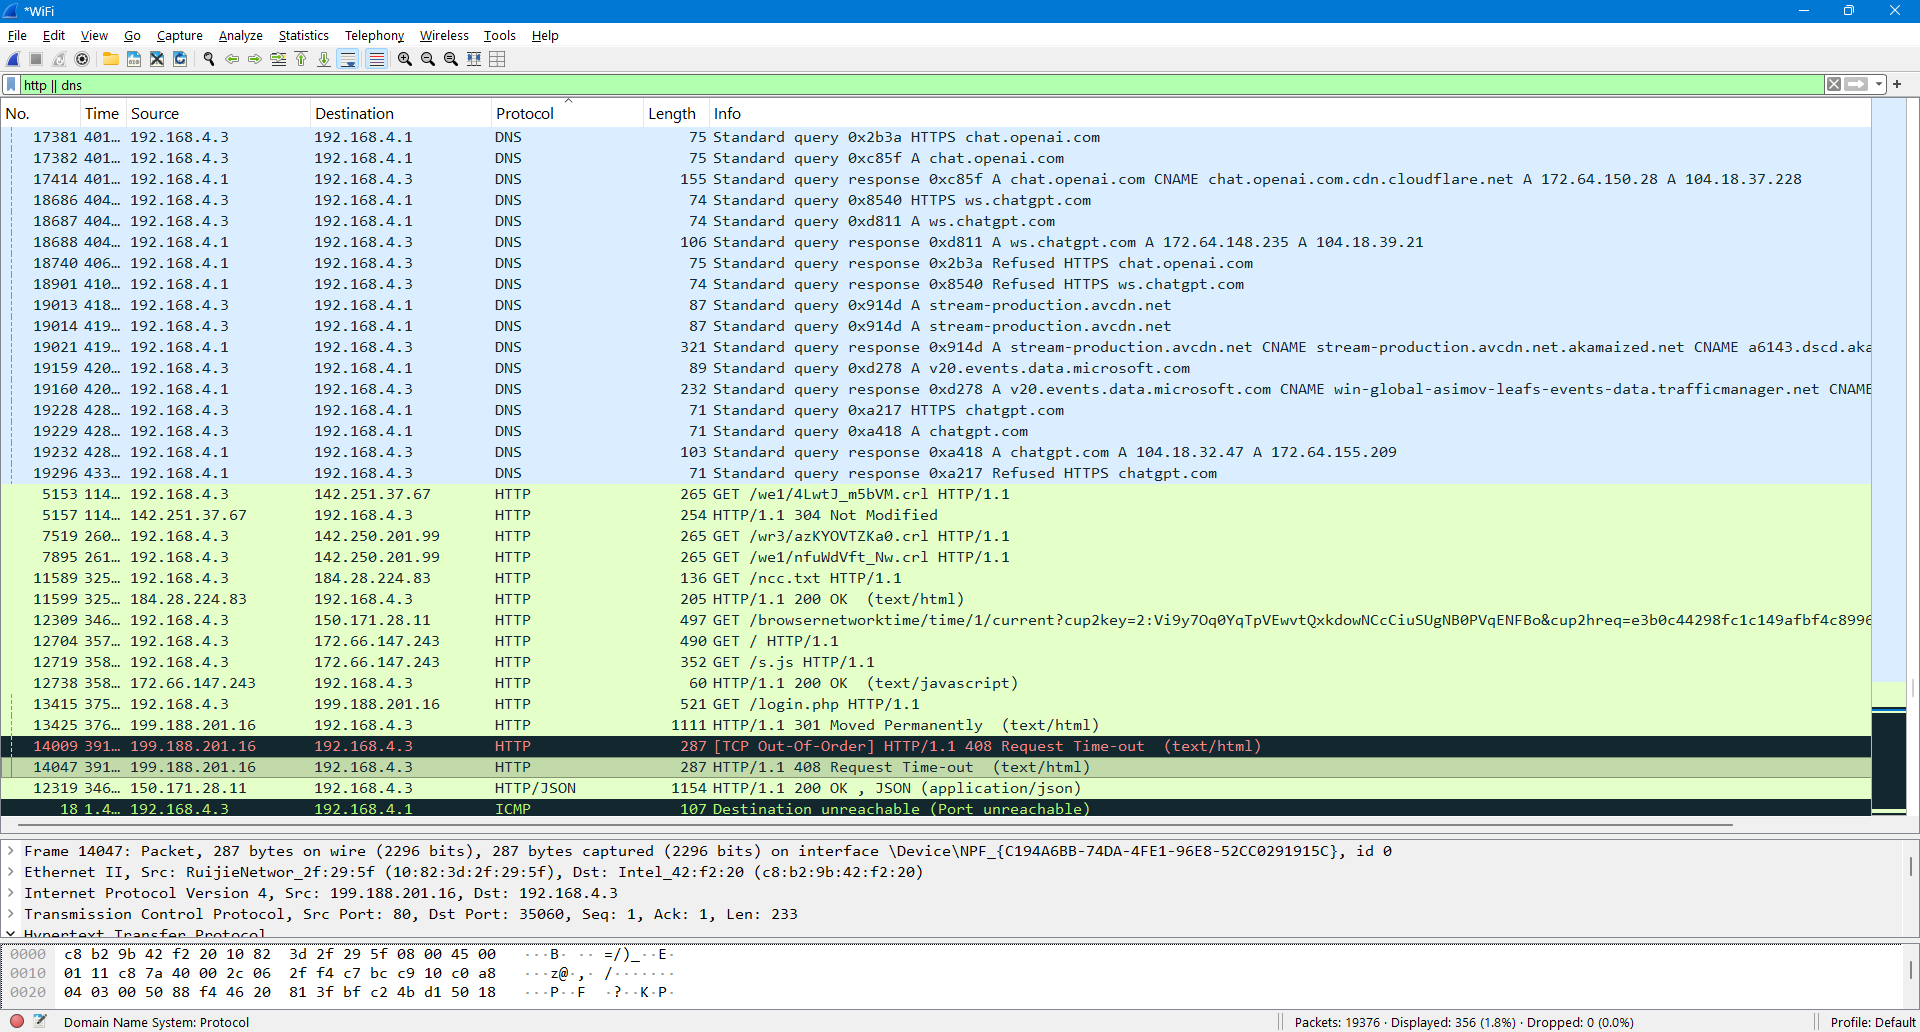
Lab 1: Follow TCP Stream
Capture web traffic and use Follow TCP Stream to find the page that carries a hidden note.
Lab 2: Catch the Call Scammer (VoIP call replay)
Find a VoIP call in the capture, play it back and answer questions about it.
Lab 3: HTTP Plain Text Credentials
Find a staff sign-in sent over HTTP and read the username and password in plain text.
Lab 4: How to capture Packets on your Network & PC?
Capture your own Wi-Fi traffic while you open a website. Find your IP, the DNS server, the website IP, the Server Name, the server port and the TLS version.
Lab 5: How to analyze a PCAP file?
Open a saved capture of microsoft.com and answer the same kind of questions offline.
Unzip the PCAP file before you open it in Wireshark.
How to submit
When you have finished all 5 labs, submit your work through the normal internship submission workflow on the submission page.
networkwalks.com/submission/Wireshark Complete Course (free)
Watch this video first.
VIDEOWireshark introduction

VIDEOWireshark introduction
How to ask Questions?
Write your question in the comments of the YouTube video above and the instructor or technical manager will answer there directly.

© All Rights are reserved, Networkwalks
Contact us today for your Cybersecurity & Network consultancy or your next training course & certification on
Cisco CCNA, Cybersecurity, Ethical Hacking, Python programming, Linux & AI.
+27 766 222 218 | +27 788 220 600
Leave your feedback at: info@networkwalks.com. Your technical questions, comments & suggestions are always Welcomed.